The European Pirate Party has submitted its response to the European Commission’s consultation on the Cloud and AI Development Act (CADA).
Published on 3 June 2026 as the centerpiece of the Commission’s Tech Sovereignty Package, CADA aims to triple EU data center capacity within five to seven years and create a four-level cloud sovereignty framework for public bodies. It aims to reduce Europe’s dependence on a handful of non-EU providers, estimated to control over 70% of the European cloud market. In a bird’s-eye view, the core pillars of the CADA are:
- Research, Development and Innovation
- Capacity Expansion
- Digital Sovereignty and Autonomy
As a political organization that has always rooted for Europe’s digital sovereignty, the European Pirates support this goal. Europe faces a real shortfall in cloud and AI computing capacity, and we welcome the Act’s “open source first” language, its Euro Cloud Federation, and its funding for green compute research.
However, building capacity is not the same as building sovereignty.
As it stands, CADA could expand Europe’s infrastructure using the same market setup that led to today’s reliance on a few large companies, instead of changing it.
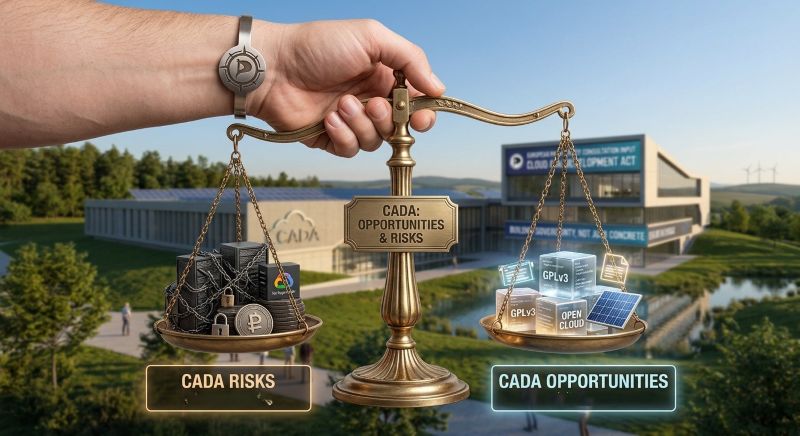
Here is a quick look at our core concerns, the opportunities we see, and how you can read our full, detailed analysis.
The Bright Spots: What CADA Gets Right
We see real opportunities in CADA that are worth building on:
- The Euro Cloud Federation (Articles 34–36): Provides a valuable public-sector alternative to commercial hyperscalers through the voluntary sharing of public data centre and cloud capacity between Union entities and Member States.
- Green Compute Leadership Initiatives (Title II): Directs vital public research funding toward energy and water-efficient data centre technologies, cutting-edge cooling, and waste-heat recovery.
- Institutionalizing Open Source (Articles 41–44): For the first time, open-source public procurement is formally included in a binding cloud policy, supported by the EU Open-Source Solutions Catalogue.
Where CADA Falls Short: Our Key Concerns
Keeping these positive elements in sight, our formal response identifies five critical structural risks:
- No Transparency on Who Benefits: The Act facilitates massive private investments and fast-tracked data centre “acceleration zones,” but fails to require public disclosure of which specific companies and projects benefit, under what conditions, or what they must deliver in return.
- Fast Permits Without Environmental Safeguards: The tripling target is being pushed at a frantic pace. By moving environmental and grid scrutiny to an aggregated zone-level before individual projects or investors are even known, the Act makes it extremely difficult for local communities and civil society to participate in meaningful oversight.
- Sovereignty on Paper, Not in Practice: The four-tier cloud sovereignty framework focuses heavily on jurisdiction, ownership, and supply-chain control to keep data away from “disqualified outsiders”. However, it does not require a compliant provider’s own systems to be architected so that the provider (or an EU public authority via lawful process) is technically blocked from reading customer data.
- Hyperscalers Win, SMEs and Open Source Wait: Mainstream market rules and fast permits are easily captured by existing capital-heavy incumbents. Meanwhile, provisions supporting innovative SMEs, multi-vendor architectures, and open-source standards remain voluntary “encouragements” rather than binding obligations.
- Green Ambitions Left as Options: While CADA talks about climate neutrality and open source in its recitals, the operative legal articles treat them mostly as voluntary goals rather than enforceable duties.
Read the Full Submission
Digital infrastructure is a common good. If Europe is going to invest billions in expanding its cloud and AI capabilities, that growth must be transparent, environmentally sustainable, and genuinely open to SMEs, cooperatives, and open-source communities, not just a new set of corporate monopolies.
European Pirates have submitted a full in-depth analysis and recommendations to the European Commission to fix the gaps – ranging from mandatory public registries for state-backed projects to binding open-source-first procurement rules.
Click here to read our full formal submission:
0 comments on “Cloud and AI Development Act – Identifying Opportunities and Analyzing Risks”